Every year, public sector cybersecurity leaders gather to tackle the most pressing challenges facing government technology. This year, the 3rd Annual GovRAMP Cyber Summit promises to be the most important yet. If you work in government IT, cloud security, or public sector compliance, this event deserves a spot on your calendar.
This guide covers everything you need to know, from dates and location to the agenda, speakers, and practical travel tips.
What Is the GovRAMP Cyber Summit?
The GovRAMP Cyber Summit is a national gathering of public and private sector leaders. It focuses on improving cybersecurity across state, local, tribal, and education governments. The event creates space for honest conversation about real challenges. Budget pressures, workforce shortages, and growing compliance demands are all on the table.
The theme for 2026 is simple but powerful: More Security. Less Burden.
This reflects a growing need among government agencies. They want stronger security outcomes without adding unnecessary operational friction. Discussions center on practical, risk-based approaches that actually work at scale.
Event Dates and Location
The 2026 edition runs from November 15 to November 17, 2026. It takes place at the Henry B. González Convention Center in San Antonio, Texas.
| Detail | Information |
| Event Name | 3rd Annual GovRAMP Cyber Summit |
| Dates | November 15–17, 2026 |
| Venue | Henry B. González Convention Center |
| Address | 900 E Market St, San Antonio, TX 78205 |
| Format | In-person only |
| Dress Code | Business casual |
San Antonio International Airport (SAT) is the recommended airport for attendees flying in. The venue is well-connected and easy to navigate. Additionally, GovRAMP has secured a discounted hotel room block at Plaza San Antonio Hotel and Spa, Autograph Collection, located at 555 S Alamo St. This hotel is also where GovRAMP member meetings will take place.
Who Should Attend?
This summit is designed for a specific community of professionals. However, newcomers to government cybersecurity are equally welcome. Sessions are structured to deliver value at every experience level.
The following groups are encouraged to attend:
- State, local, tribal, and education (SLTE) government leaders
- Chief Information Officers (CIOs)
- Chief Information Security Officers (CISOs)
- GovRAMP members and partners
- Technology providers serving the public sector
- Procurement and risk management professionals
- Cybersecurity consultants and compliance experts
Whether you are just beginning your GovRAMP journey or are deeply experienced, the program offers relevant sessions for your level.
Day-by-Day Agenda Overview
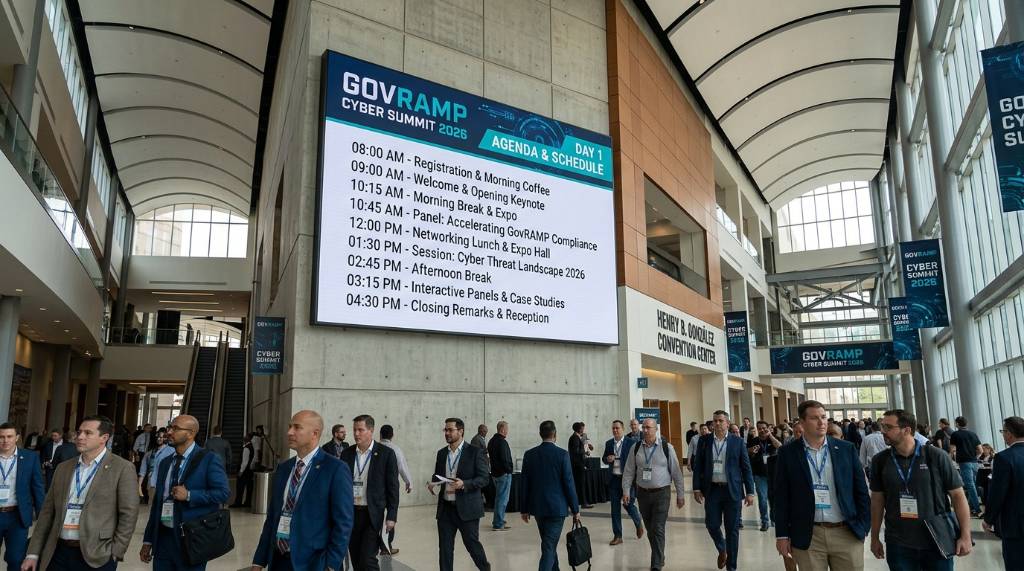
The three-day schedule is thoughtfully structured. Each day serves a distinct purpose, building toward a complete experience.
Day 1 — Sunday, November 15, 2026 (Member-Only Sessions)
Day 1 programming runs from 3:00 PM to 5:00 PM Central Time. It is exclusively reserved for GovRAMP members and invited guests.
Key sessions include:
- Direct engagement with GovRAMP leadership
- A preview of upcoming program updates
- An open member discussion to shape the future of the program
- Peer-to-peer sharing of implementation strategies
The General Session on Day 1 focuses on building a GovRAMP Validated Architecture. The session title is “From ATO to Assurance.” It challenges attendees to move beyond compliance and build systems that support continuous security and resilience.
Day 2 — Monday, November 16, 2026 (Main Conference Day)
Day 2 is the heart of the summit. Registration opens in the morning, and the full program runs throughout the day.
Highlights include:
- General Session: National Leaders on How GovRAMP Helps Modernize Efficiently
- Breakout B1: GovRAMP Tools That Solve Each Gap
- Ready-to-use templates, evaluation tools, and procurement contract language
- The GovRAMP Founder’s Award Presentation
- Breakout C3: Cyber Unplugged (No Slides format)
The “Cyber Unplugged” session is particularly notable. It strips away presentations and invites open, candid conversation. Therefore, it tends to be one of the most engaging parts of the event.
Day 3 — Tuesday, November 17, 2026 (Closing Day)
Day 3 wraps up with reflection and forward momentum.
Highlights include:
- Fireside Chat: Texas Leaders on Whole-of-State Cyber Defense
- A closing session to review key summit insights
- Open conversation and connection opportunities for future collaboration
Key Themes and Topics
The 2026 agenda is built around three main areas of focus. These themes run through nearly every session and discussion.
| Theme | What It Covers |
| Framework Alignment | GovRAMP, FedRAMP, and CJIS integration strategies |
| Risk-Based Security | Practical approaches that reduce burden without reducing protection |
| Workforce and Resources | How agencies do more with limited staff and tighter budgets |
One of the most important conversations involves framework alignment. Sessions will explore how GovRAMP, FedRAMP, and CJIS standards can work together. The goal is to reduce duplication and support reciprocity between programs. This matters because agencies often spend significant time and money on overlapping compliance work.
Additionally, emerging cyber risks will be discussed. Attendees will gain insight into threats that are evolving faster than most agencies can track. Practical tools and templates are also available throughout the event to help teams put concepts into action immediately.
Confirmed Speakers
Several prominent voices have already been confirmed for the 2026 summit. Public listings name five speakers from key government and industry roles.
Confirmed speakers include:
- Bernice Russell-Bond, CISO, State of North Carolina
- Tony Sauerhoff, Executive Director and State CIO, Texas Department of Information Resources (and GovRAMP Board President)
- J.R. Sloan, a GovRAMP co-founder and past president
These speakers bring a combination of executive leadership and deep technical expertise. Their sessions are designed to be direct, practical, and grounded in real-world experience.
Sponsors and Partners
The 2026 summit is supported by more than 22 sponsor and partner organizations. Carahsoft serves as the presenting sponsor, reflecting its long-standing role in supporting government technology initiatives.
Other notable sponsors include Fortinet, Rubrik, Extreme Networks, Tenable, BeyondTrust, Coalfire, Tanium, Axonius, Keeper, and Orca Security. Companies like Second Front, Paramify, RegScale, and RISCpoint also appear as workshop and learning lab sponsors.
These partnerships help fund high-quality programming and ensure that technology demonstrations reflect tools agencies can actually use.
Registration Guide
Registration for the 2026 summit is now open. The process is straightforward, and several options are available depending on your role.
| Attendee Type | Registration Details |
| Public Sector (Government) | Complimentary registration |
| Private Sector / Industry | Standard registration fee applies |
| GovRAMP Members | Member rate (TBA) |
| Scholarship Applicants | Contact info@govramp.org |
Public sector registration is offered at no cost. Therefore, government employees face no financial barrier to attending. For private sector professionals, the standard registration fee applies. GovRAMP has not yet announced a specific group rate, so checking the official website for updates is recommended.
Scholarship opportunities are available for eligible public sector professionals who need additional support. Reaching out to GovRAMP directly at info@govramp.org connects you with the team for details.
Once your registration fee is fully paid, access to all summit sessions, activities, and GovRAMP session materials is included.
CPE Credits
Continuing Professional Education (CPE) credits are available at this event. Eligible sessions qualify for credit, making the summit valuable for credentialed security professionals who need to maintain certifications. Further details on eligible sessions can be found on the official summit website.
Networking Opportunities
The summit includes multiple structured and informal networking opportunities throughout all three days. These range from peer discussion groups to exhibitor floor conversations and speaker meet-and-greet moments.
Networking is built into the schedule, not treated as an afterthought. However, some of the best connections happen during unstructured breaks and social events. Coming prepared with clear goals for whom you want to meet will help you make the most of your time.
Practical Travel Tips for Attendees
Planning your trip early makes a big difference. Here are some practical considerations:
- Fly into San Antonio International Airport (SAT), as it is the closest and most convenient airport
- Book your hotel room in the GovRAMP group block at Plaza San Antonio Hotel and Spa to get the discounted rate
- Dress code is business casual throughout the event
- Arrive on Sunday if you want to attend the member-only Day 1 sessions
- Bring business cards or a digital contact-sharing method for networking
- Register early since session seats may fill up
Why This Summit Matters in 2026
Government cybersecurity has never been more complex. Agencies face more threats, fewer resources, and higher expectations than ever before. Events like this summit create space to slow down, think clearly, and learn from peers who face the same problems.
The conversations happening at this summit shape policy, procurement decisions, and security strategies across the country. Therefore, attending is not just professional development. It is participation in the direction of public sector security itself.
Conclusion
The 2026 GovRAMP Cyber Summit is a critical event for anyone working at the intersection of government and cybersecurity. Scheduled for November 15 through 17, 2026, at the Henry B. González Convention Center in San Antonio, Texas, the summit brings together CIOs, CISOs, government leaders, and technology providers under one roof.
The three-day agenda is structured to move from member strategy on Day 1 to national conversations on Day 2 and state-level insights on Day 3. Key themes include framework alignment across GovRAMP, FedRAMP, and CJIS, risk-based security approaches, and workforce solutions for resource-constrained agencies.
Registration is open now, with complimentary options for public sector professionals. CPE credits, scholarship opportunities, and discounted hotel accommodations are also available. Whether you attend for the sessions, the speakers, or the networking, this summit offers real value for anyone committed to improving government cybersecurity.
Frequently Asked Questions (FAQs)
When is the 2026 GovRAMP Cyber Summit?
The summit takes place from November 15 to November 17, 2026.
Where is the event held?
The event is held at the Henry B. González Convention Center, 900 E Market St, San Antonio, TX 78205.
Is the summit in person or virtual?
The 2026 summit is in-person only. There is no virtual or hybrid attendance option this year.
How do I register for the summit?
Registration is open on the official GovRAMP website. Public sector attendees can register for free, while private sector professionals pay a standard registration fee.
Are CPE credits available?
CPE credits are offered for eligible sessions. Details are available on the official summit website.
Who are the target attendees for this event?
The event is designed for government CIOs, CISOs, procurement leaders, risk professionals, GovRAMP members, and technology providers serving the public sector.
Is there a discounted hotel rate for attendees?
GovRAMP has secured a group rate at Plaza San Antonio Hotel and Spa. The specific rate is to be announced, so checking the official site for updates is recommended.
What airport should I fly into?
San Antonio International Airport (SAT) is the recommended airport for attendees traveling by air.
Are scholarships available for the summit?
Scholarship opportunities exist for eligible public sector professionals. Contact info@govramp.org for information.
What is the dress code for the summit?
Business casual attire is recommended throughout the event.
